 Tiva Creative
Backend Engineer
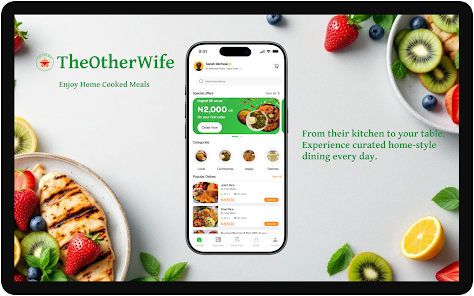
Built the client-facing API for The Other Wife — a home-chef food-ordering app — covering auth, location search, real-time ordering and a tamper-proof payment ledger.
stack
overview
The Other Wife connects customers to verified home chefs nearby. The backend powers auth, the meal-and-vendor catalog, location-based search, ordering, live order status and a tamper-proof payment ledger — the stable contract every client built on top of.
how it works
01 · Authentication & Sessions
Sign-in combines email + OTP with short-lived JWT access tokens and rotating refresh tokens, so sessions recover without re-entering passwords and exposed tokens expire fast.
02 · Catalog & Location Search
Meals and home-chef vendors are indexed by geolocation. Customers set a radius and the API returns nearby vendors within it — a bounding-box prefilter followed by haversine refinement — so discovery tracks the user's immediate area.
03 · Ordering & Real-time Updates
The cart → order lifecycle runs through a RESTful flow, with status transitions (placed, confirmed, preparing, en-route) pushed to clients over WebSockets so the order screen updates live without polling.
04 · Tamper-proof Payment Ledger
Every payment entry is hash-chained, then anchored to an external checkpoint — structured logs plus a daily cron and an on-demand admin endpoint — so a full database wipe-and-regenerate can't forge a consistent history.
05 · Deployment
Containerized with Docker and served behind an Nginx reverse proxy, with environment-driven configuration and deploy scripts for reproducible rollouts.
01 · Requirement Analysis
The Other Wife, a home-chef food-ordering app, needed a dependable client-facing API: auth, the meal-and-vendor catalog, location-aware search, ordering with live status, and a payment history customers and chefs could trust.
02 · Architecture Discovery
Modeled the domain as home chefs → meals → cart → order → payment ledger, with role scopes for customer, chef and staff. Chose a REST resource layout, validated the data flow against the app screens, and decided where real-time push (WebSockets) and integrity (hash-chained ledger) had to live.
03 · Software Architecture
A layered TypeScript service — routes → controllers → services — over MongoDB, with OTP + JWT access/refresh auth, a WebSocket gateway for live order updates, a hash-chained payment ledger with external checkpointing, and a Docker image behind Nginx for deployment.
04 · Development Principles
Idempotent order creation, validation-at-the-boundary, WebSocket reconnection with backoff, the ledger hash-chain plus an external anchor, environment-driven config, and reproducible container rollouts.
05 · Impact
Shipped the backend the team built on top of, with a stable contract that survived multiple app iterations and a payments history hardened against tampering.